Release preflight for game mods & mod packs
Scan a folder or ZIP before you publish. Catch packaging risks, leaked secrets, and missing metadata — and share a clean report with your players.


Scan a folder or ZIP before you publish. Catch packaging risks, leaked secrets, and missing metadata — and share a clean report with your players.
descriptor.mod checkssupported_version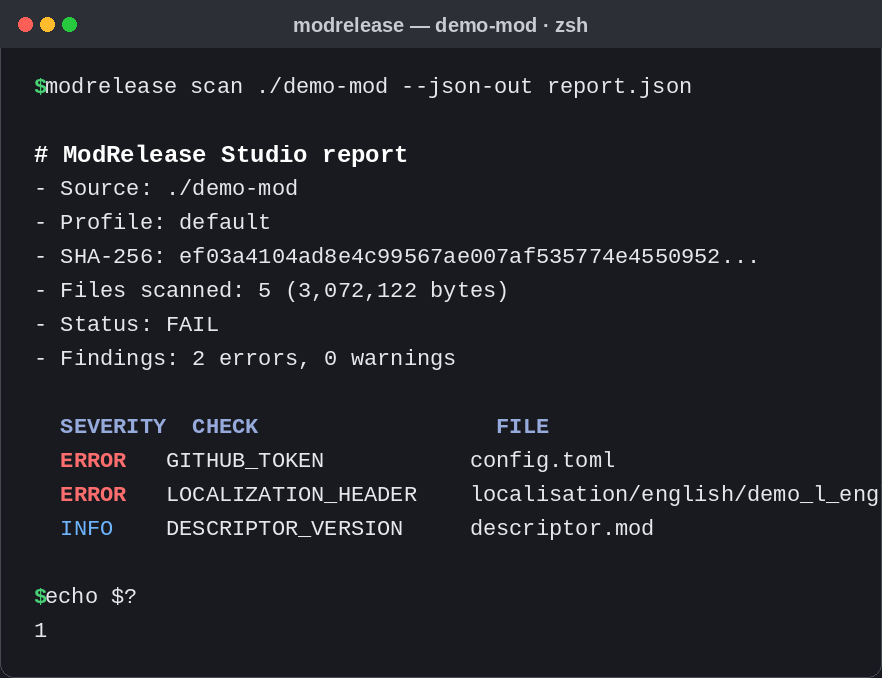
# Before your first release
modrelease scan ./my-mod --md-out release-report.md

# Compare two builds
modrelease compare ./previous-build ./candidate-build

# Or gate releases in CI with the GitHub Action
- uses: GhosTnever-lkm/modrelease-studio-action@v1
Exits with code 0 (ready), 1 (release-blocking findings), or 2 (invalid input). Requires Python 3.11+, standard library only.
MIT-licensed CLI. Scan, compare, JSON/Markdown reports. Run locally or in CI.
Custom rule packs, team reporting, release dashboards. Join the waitlist via contact.
Custom checks, release audits, and gate setup for your mod distribution.
Questions, custom checks, or a release audit? Reach out by GitHub or email.